Insider Threat & Social Engineering Overlap
Insider threat concerns the risk posed by people or entities with authorised access, organisational knowledge or a trusted relationship. Social engineering concerns the use of influence, deception or manipulation to shape behaviour. They intersect where an insider’s access, knowledge or trusted position is used, whether deliberately or through manipulation, to influence decisions, circumvent security controls or cause harm to organisational operations, assets or individuals.
Current staff, contractors, former personnel and other trusted third parties may possess authority, working relationships, organisational knowledge or residual access that an external actor would need to imitate or acquire. Social engineering techniques and manipulation levers can therefore be applied from within, or through trusted relationships, with less likelihood of triggering controls designed primarily to detect external threats. Authority may be genuine rather than impersonated, and information that would otherwise require reconnaissance may already be available through the person’s role or prior association.
The diagram below shows how insider access, knowledge and trusted relationships can combine with social engineering methods to circumvent organisational controls and manipulate established processes.
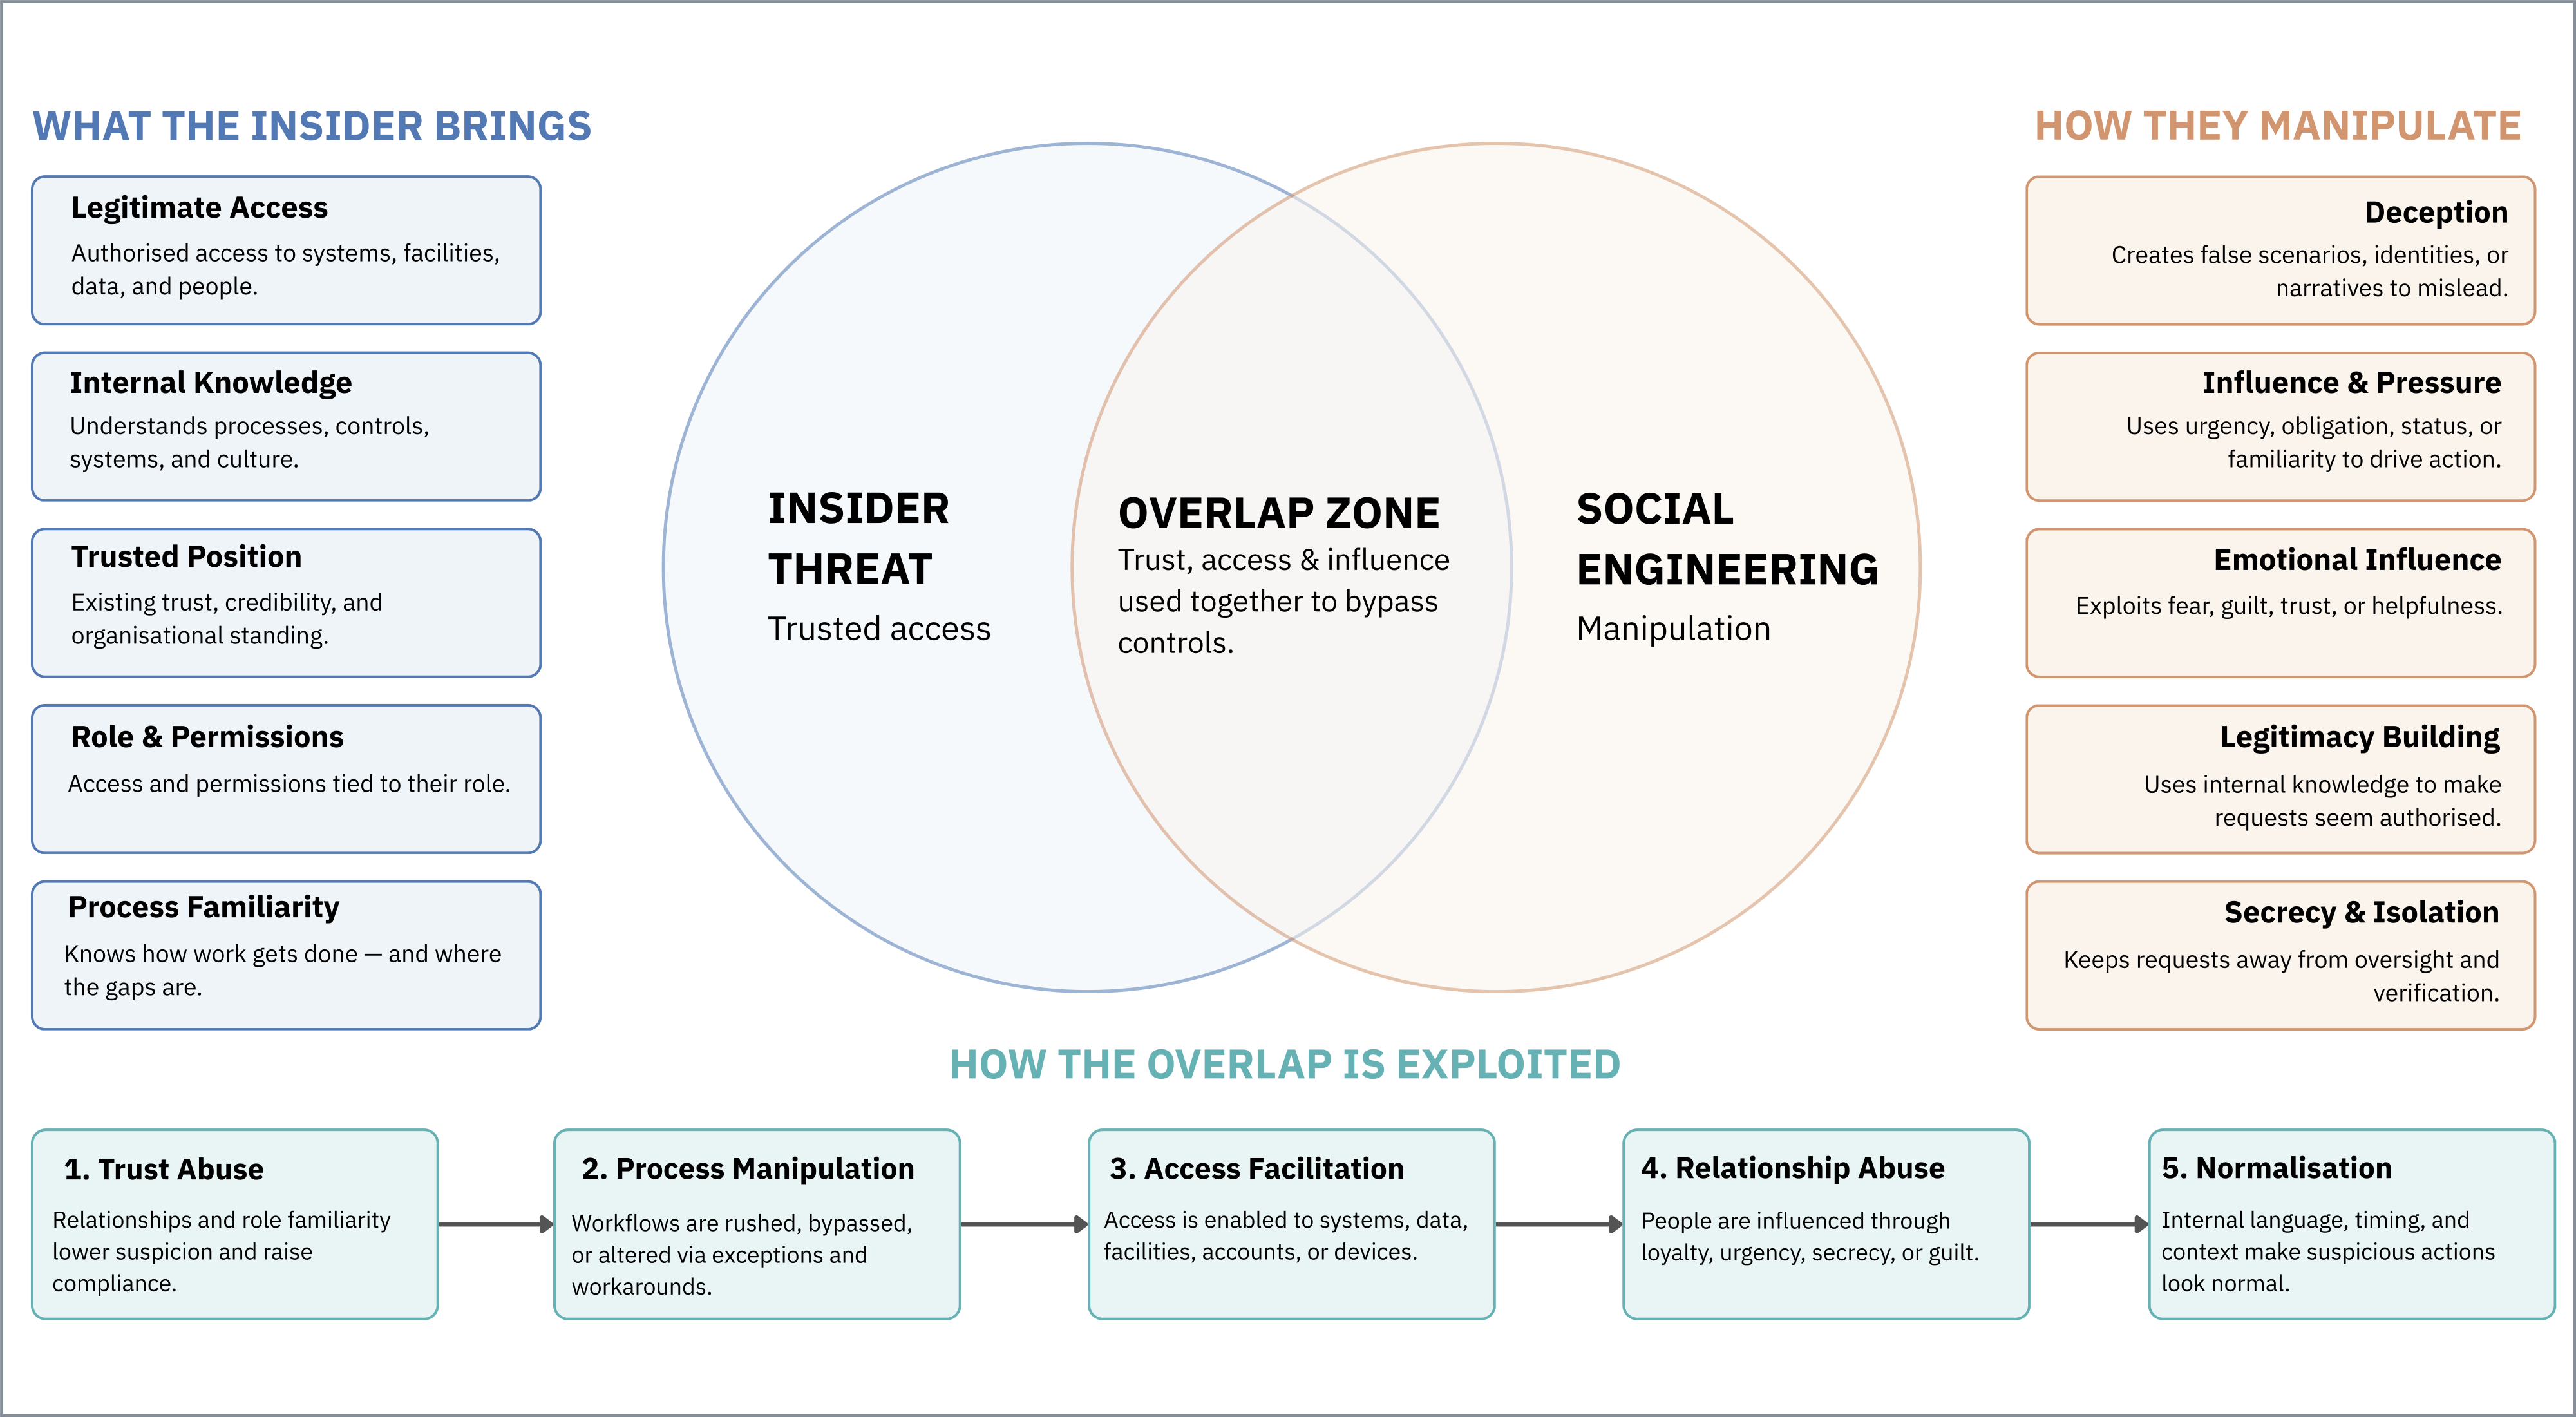
Insider threat and social engineering overlap when trusted access, internal knowledge, influence and process abuse are used together.